Zero-Trust Network Architecture Design & Deployment

Zero-Trust Network Architecture Design & Deployment - 1

Details

Options
Firewalls, Monitoring
Company Name
OTHEE TECHNOLOGIES
Specialization
Cybersecurity & Data Protection
Type of Service
Programming & Tech

Zero-Trust Network Architecture Design & Deployment Highlights

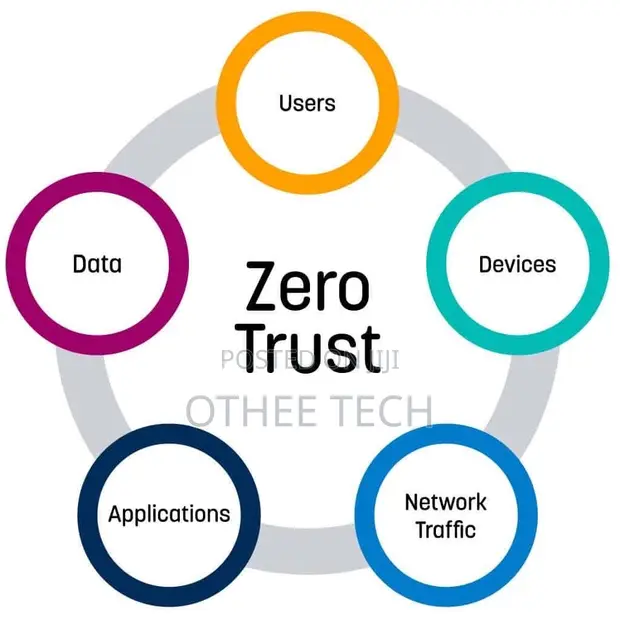
  • Enhanced Security Posture: Zero-Trust Network Architecture fundamentally shifts security from perimeter-based to identity-centric. It assumes no user or device can be trusted by default, requiring strict verification for every access attempt.
  • Micro-segmentation Capabilities: This approach enables granular control over network access by dividing the network into small, isolated segments. This limits the lateral movement of threats if a breach occurs.
  • Continuous Monitoring & Verification: Zero-Trust relies on constant monitoring of user and device behavior, along with continuous re-authentication. This ensures that access privileges are always appropriate and up-to-date.
  • Reduced Attack Surface: By enforcing least privilege access and segmenting the network, Zero-Trust significantly reduces the potential pathways for attackers to exploit vulnerabilities.
  • Adaptable to Modern Workloads: This architecture is well-suited for today's dynamic environments, including cloud computing, remote workforces, and BYOD policies, by providing consistent security regardless of location.

Description

• Design and deployment of Zero-Trust security architectures. • Enforces identity-based access, least-privilege controls, and network segmentation. • Continuous verification of all network access requests. • Specialization in Cybersecurity & Data Protection. • Services include firewall implementation and network monitoring. • Suitable for organizations seeking advanced network security. • Offered by OTHEE TECHNOLOGIES, with expertise in IT services.